The Engineering Desk / Module 05
Certification & audit defence
Certificates that can be rebuilt from the record years later — four-eyes on approval, period locks after close, and an audit trail nobody can edit.
- Certifier
- Internal audit
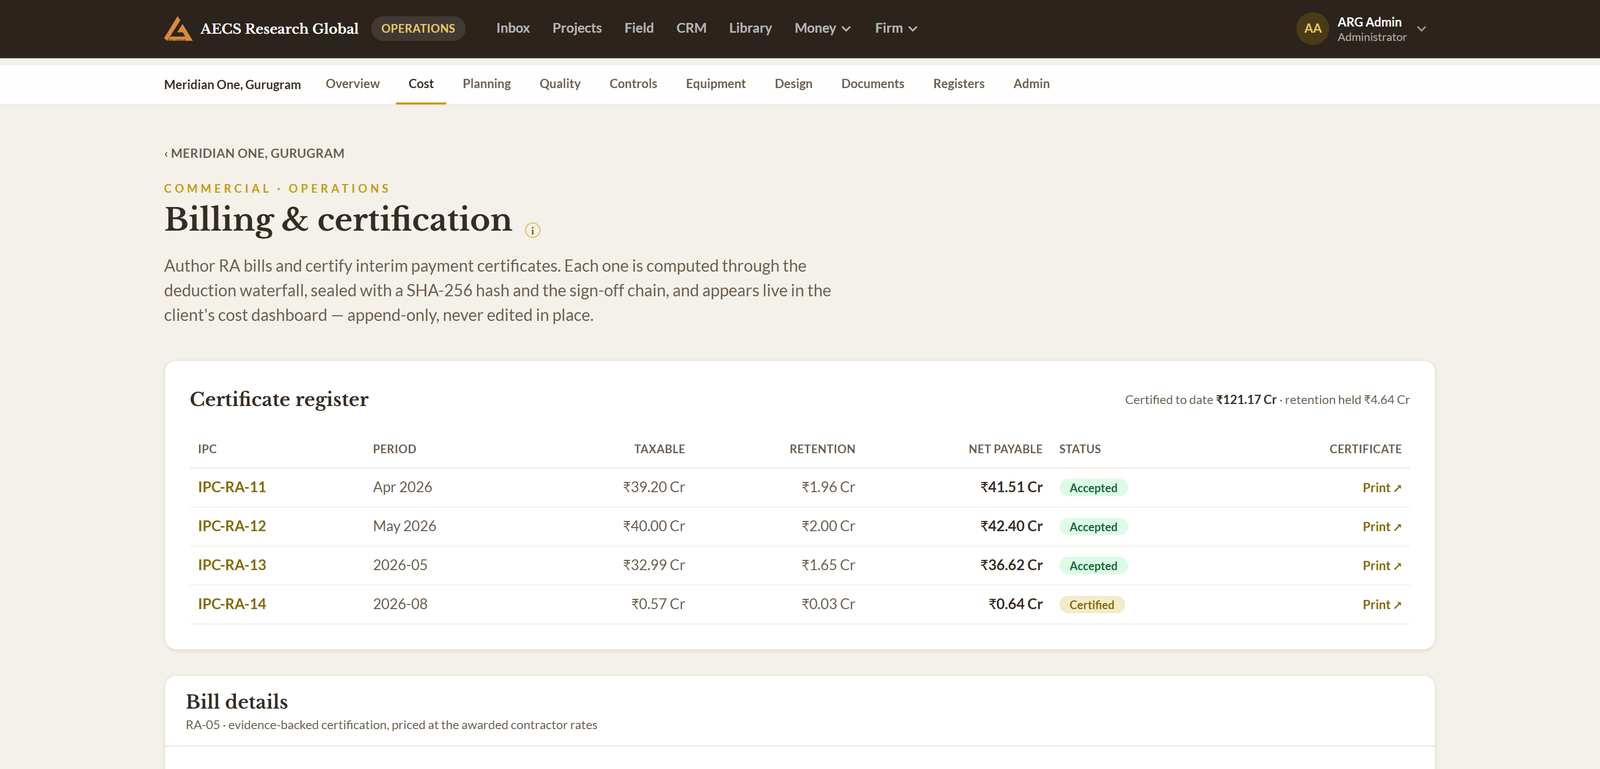
On this desk. For government and institutional work, the audit para arrives long after the people have moved on. The only defence that survives is a record where the certificate, the measurement behind it and the authority that approved it are all still present and unaltered.
What it holds
Server-enforced separation of duties
The certifying authority is bound to the session that certifies. Nobody approves their own submission, and the check is in the server, not in a policy document.
Period locks
A closed month is closed. Adjustments belong to the open period with their own reference, which is what makes a monthly figure quotable six months later.
Immutable audit events
Every privileged action recorded as an append-only event with actor, time and payload — readable in the application rather than extracted from server logs by an engineer.
Row-level access on the money plane
A user scoped to one project cannot read or act on another, enforced at the database. Confidentiality between mandates is a property of the storage, not of the interface.
What it produces
- Certificate reproducible from its underlying records
- Audit-event extract for a specific document or period
- Backup and restore evidence — proven by a drill, not asserted
What it will not allow
- Editing a closed period
- Deleting an audit event, at any privilege level
- Acting on a project you are not scoped to